

Company

Restrict unneeded access in AWS via self-serve access requests, flexible policy workflows, and automated provisioning.
Users request access, and approvers get notified through Slack, MS Teams, or Jira, creating a seamless experience. Requests include all necessary information for approvals, reducing back-and-forth iterations.
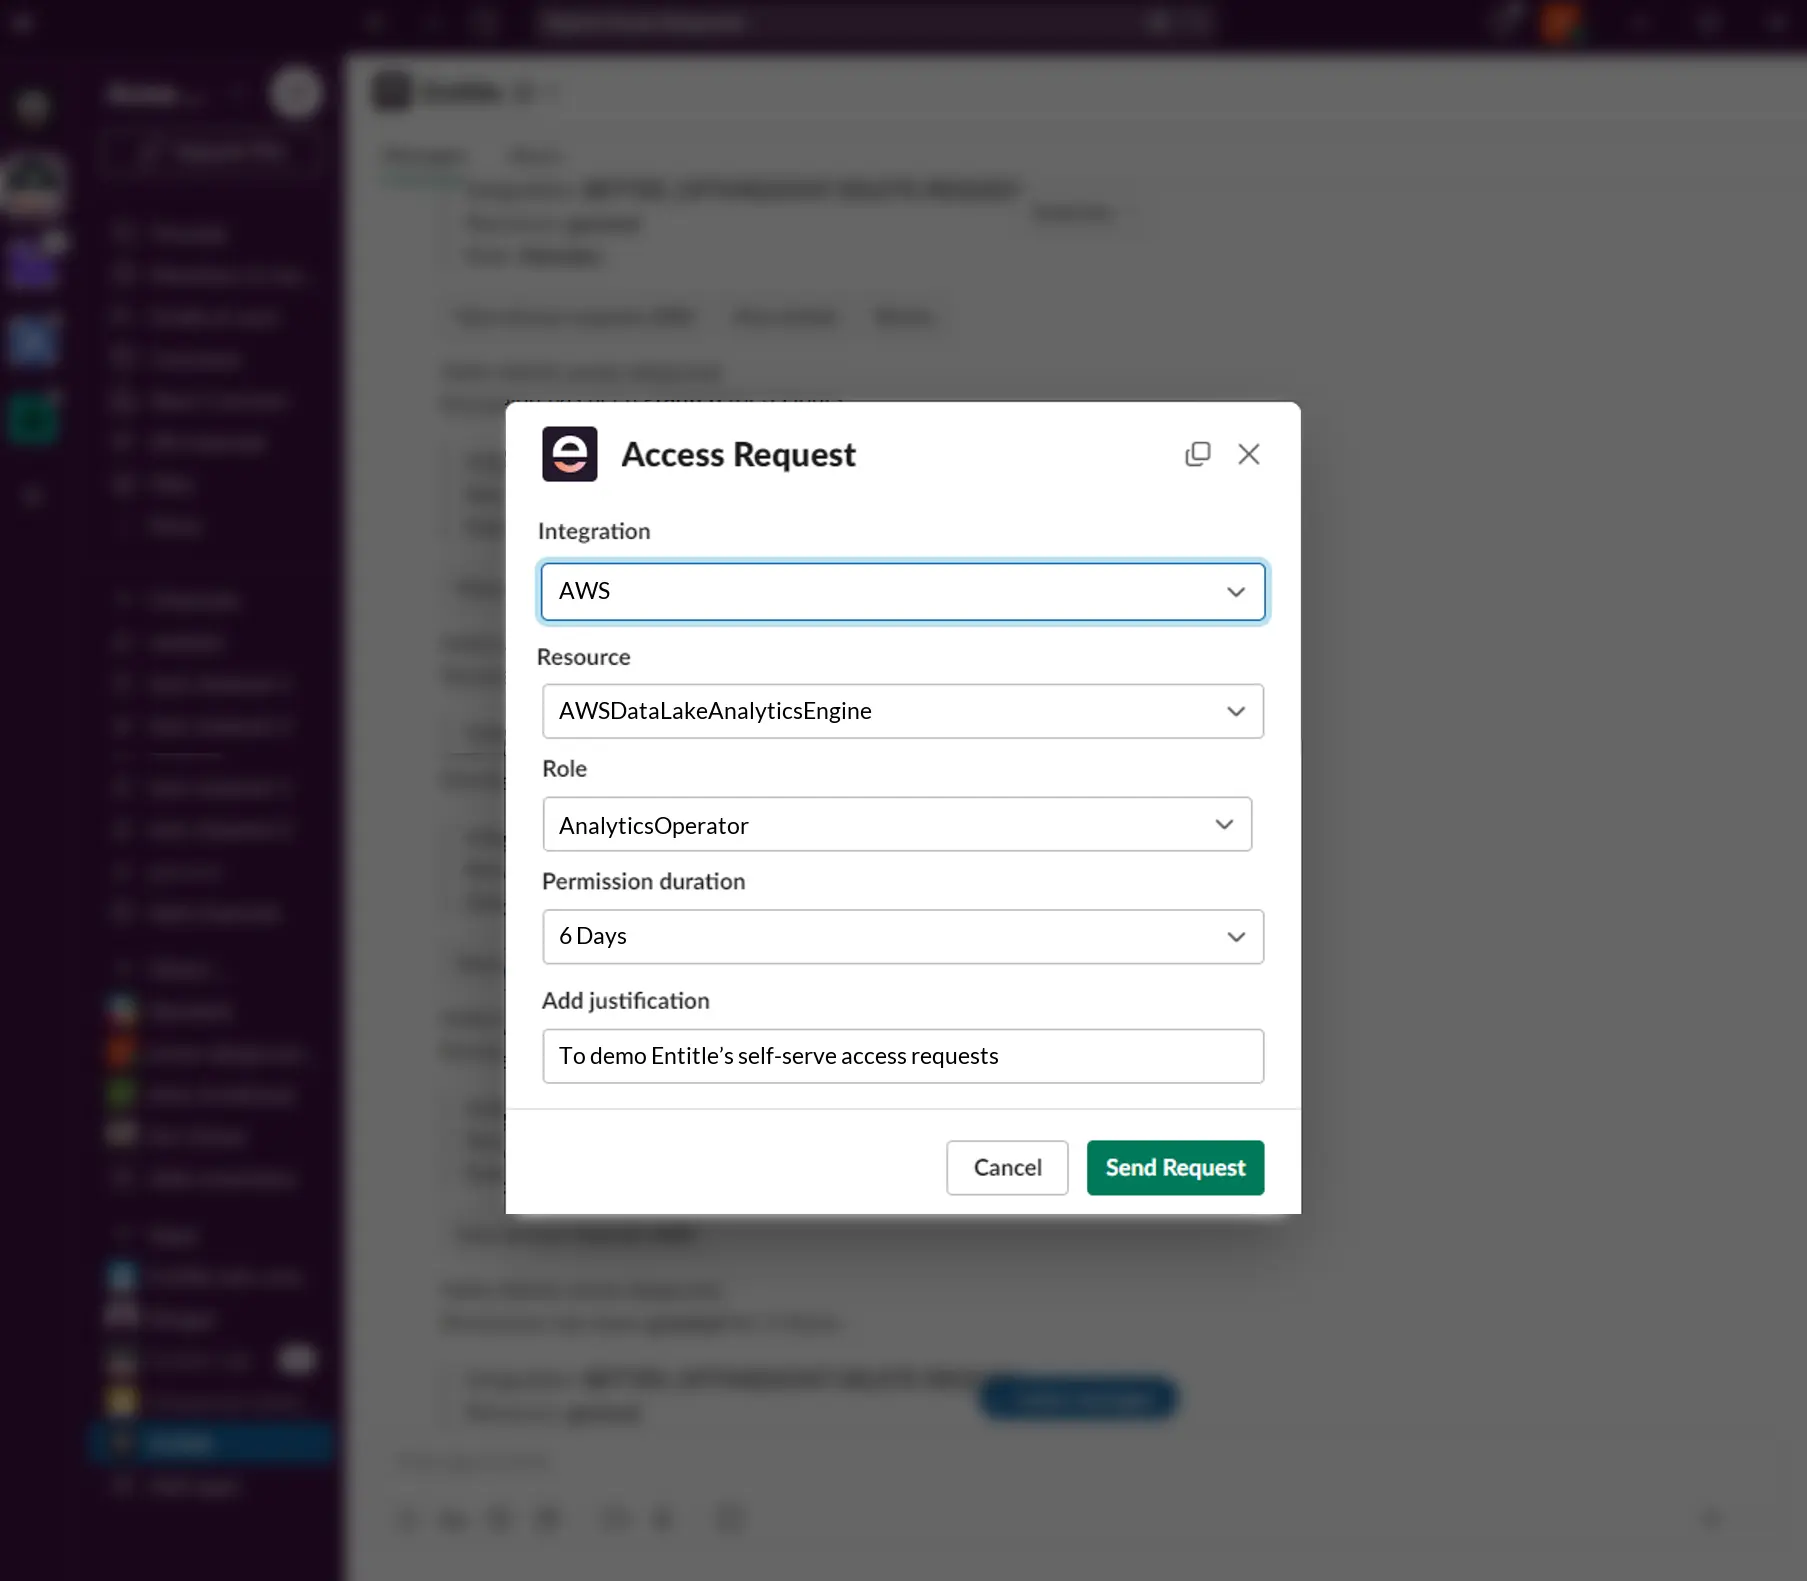

In one request, employees can get just in time access to assets from different applications like AWS S3 buckets, MongoDB collections, SharePoint folders, and Slack channels.
Assign dedicated approvers for access requests: managers, app owners, groups or others. Upon approval, provisioning occurs automatically, and deprovisioned when expired.


Designed for simplicity and flexibility, you can easily view users, identities, integrations, resources, and roles. Administrators gain powerful visibility, overseeing all permissions, including ones that were not granted through Entitle.
"I like Entitle because it’s one of those tools I can set up and forget about. I never have to go into it and it just works."

Mike Morrato
CISO and Global Head of IT,
Noname Security
Use a centralized view to understand who was granted access to what resources, who authorized it, the justification, the duration, and the exact timing. Track user activity within the third-party applications, ensuring compliance and integrate with your SIEM.


Use Entitle’s APIs and Terraform Provider to manage access controls using Infrastructure-as-Code (Iac). Customize our solution to fit your environment.


